
WEDOS IP Addresses
For WEDOS.protection to work optimally, the origin web server should accept incoming traffic only from the WEDOS.global Anycast proxy network. Whitelisting these IP addresses on the origin server ensures that the origin server can properly recognize all legitimate traffic, and reject requests from any other source before reaching your application.
This approach closes the most common bypass route used by attackers, and guarantees that every request passes through the WGP proxy, where filters, WAF, GeoIP, and other protection mechanisms are applied.
Why Whitelisting WEDOS IPs Matters
When DNS records point to the WGP proxy, all legitimate visitor traffic is routed through the Anycast network before reaching the origin server. However, if the origin server still accepts traffic from any IP address, attackers who discover the server’s IP can connect directly and bypass WEDOS.protection entirely.
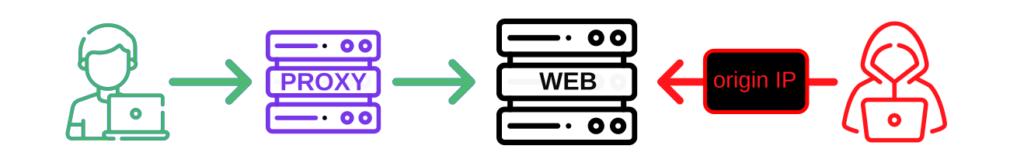
To prevent this, configure the origin server to accept connections only from the official WEDOS.global IP ranges. This ensures:
- Full traffic inspection. WGP analyzes, filters, and processes requests before they reach the origin server.
- Reduced attack surface. Direct connection attempts to the origin server are dropped at the network level.
- Accurate visitor identification. The origin server only handles traffic forwarded by trusted proxy nodes.
Note that if your origin server blocks WEDOS Global IP addresses for any reason, your website will become inaccessible to all visitors.
Where to Find the WEDOS IP List
WEDOS maintains an always up-to-date list of IP addresses used by the Anycast proxy network. This list is publicly available and should be used as the single source of truth when configuring the origin server.
The list is available in JSON format at https://ips.wedos.global/ips.json and in TXT format at https://ips.wedos.global/ips.txt.
Configuring the Origin Server
The exact configuration depends on the operating system, web server, and firewall used on the origin. The general principle, however, is the same in all cases:
- Retrieve the current list of WEDOS.global IP addresses from https://ips.wedos.global/ips.json or https://ips.wedos.global/ips.txt.
- Configure the firewall or web server to allow incoming connections on ports 80 and 443 only from the listed IP ranges.
- Configure the firewall or web server to deny all other incoming traffic on those ports.
- Verify that the origin server is no longer reachable directly from outside the WEDOS.global network.
This configuration applies to both IPv4 and IPv6 addresses. If the origin server uses only IPv4, apply only the IPv4 entries from the list. If the origin server supports IPv6, configure both IPv4 and IPv6 ranges.
Keeping the IP List Up to Date
The WEDOS.global IP list can be expanded as new proxy nodes are added to the Anycast network. To avoid service disruptions, synchronize the origin server configuration with the official list once or twice a day.
Common Misconfigurations
These are the most common issues with whitelisting WEDOS IPs:
- Using an outdated IP list. Static or manually copied lists can become outdated as the Anycast network grows, causing legitimate proxy traffic to be blocked.
- Restricting only one IP version. If the origin server supports both IPv4 and IPv6, configure both. Omitting one version may leave a bypass route open.
- Overlapping or conflicting firewall rules. Existing allow rules for other sources may unintentionally permit direct access. Review all relevant rules to ensure consistency.
- DNS records exposing the origin IP. Make sure that DNS records point exclusively to the WGP proxy. Any leftover A or AAAA record pointing to the origin server can cause traffic to bypass the proxy.